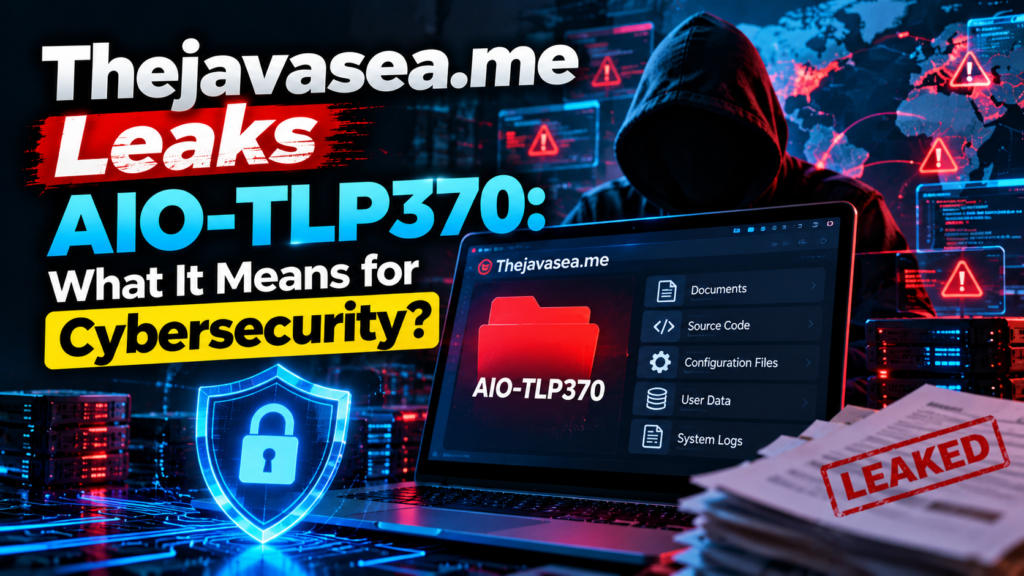
The internet tends to turn obscure terms into viral subjects quite quickly. In this regard, thejavasea.me leaks aio-tlp370 is an interesting concept that has appeared on various forums and web publications. As people attempt to understand what thejavasea.me leaks aio-tlp370 is, questions arise about its nature, credibility, and even potential damage to personal accounts and privacy.
It is crucial to address these concerns, as information about thejavasea.me leaks aio-tlp370 appears to be more speculative than factual.
While some web outlets explain thejavasea.me leaks aio-tlp370 with references to a particular leak-related package, there is no comprehensive list of its supposed contents as of now.
Some outlets explain thejavasea.me leaks aio-tlp370 with references to a software program, while others mention a particular collection of files. It is necessary to distinguish between the available facts and speculations. In this article, I will discuss thejavasea.me leaks aio-tlp370’s definition and implications for cybersecurity.
What Is thejavasea.me Leaks AIO-TLP370?
The expression thejavasea.me leaks aio-tlp370 refers to either the archive or the identifier of a particular leak-related package.
The connection with TheJavaSea.me is explained by the fact that this website name is mentioned in the second-level coverage of the data breach. TheJavaSea.me is a source of information on alleged shared files and leaks, but it does not provide official confirmation of the contents of aio-tlp370.
I think it is essential to stress that the presence of a file name, website address, or even an article does not confirm the occurrence of a cyber incident.
Many sources highlight thejavasea.me leaks aio-tlp370 as an example of confidential information, including source codes and other files that could be part of an archive. Until official information is published, these claims can only be regarded as assumptions.
For an ordinary reader, it may be helpful to separate unsubstantiated hypotheses from facts.
Breaking Down the AIO-TLP370 Name
An initial analysis of the name AIO-TLP370 can help to identify the potential source of the label’s popularity. First of all, AIO is an acronym that stands for All-In-One.
This term is common in the IT industry and refers to a package of programs, tools, or other utilities. Some web outlets suggest that AIO in AIO-TLP370 stands for All-In-One, but there is no confirmation that this is the official name of the archive.
Thus, AIO in AIO-TLP370 should be regarded as a possible designation rather than a verified fact.
As for the rest of the name, TLP370, the letters TLP indicate the Traffic Light Protocol, a special classification used to describe levels of sensitivity and sharing instructions for information. The TLP standards are divided into four categories: TLP:RED, TLP:AMBER, TLP:GREEN, and TLP:CLEAR.
On the other hand, TLP370 is not an official standard; therefore, AIO-TLP370 is not a formally structured document.
After all, confusing unofficial TLP370 and TLP:GREEN, for example, may lead to the publication of misleading articles. The importance of analyzing the details of the name lies in the fact that it does not confirm the authenticity of the leak, its content, or even its alleged source.
As cybersecurity threats continue to evolve, blockchain-based games like Play Hiezcoinx2.x9 Winning: Unlock Rewards & Earn Big in Blockchain Game also highlight the importance of understanding digital assets and online security.
Is the AIO-TLP370 Leak Confirmed?
One of the central questions related to thejavasea.me leaks aio-tlp370 is whether the leak is confirmed. In other words, it is necessary to understand whether the file is genuine and whether it really contains the information described in various articles.
From my perspective, this issue is critical to answering because most of the available web outlets lack confirmation of thejavasea.me leaks aio-tlp370 . Some articles contain duplicate information, while others contradict each other. After reading several stories about thejavasea.me leaks aio-tlp370, I managed to get an idea of why this file became popular, but not an exact understanding of its content.
Nevertheless, I do not consider this information to be false either. On the contrary, I think it is essential for readers to conduct their own research and verify the facts before drawing conclusions.
In particular, it may be helpful to pay attention to articles that provide specific statistics, such as the number of victims or the size of the archive. At the same time, people should be particularly careful about sources that do not indicate official evidence.
Potential Cybersecurity Risks of Alleged Leak Packages
Despite the lack of concrete information about thejavasea.me leaks aio-tlp370, it is crucial to discuss the potential risks related to such files. I consider it important to note that even a small amount of information from an alleged leak can be dangerous to users.
1. Malware and Malicious Downloads
Thejavasea.me leaks aio-tlp370 may contain various types of malware and malicious programs, such as information stealers or remote access Trojans. Unverified files, especially those that appear on unofficial websites, can include a wide range of threats.
In particular, ransomware can encrypt users’ data, demanding payment for its decryption. In this situation, users will have to decide whether to pay the hackers or try to remove the virus on their own. Needless to say, this scenario demonstrates how dangerous such files can be.
Thejavasea.me leaks aio-tlp370 can also contain programs that steal personal information, including photos, private messages, and payment details. In this regard, I think it is crucial to emphasize that downloading thejavasea.me leaks aio-tlp370 is not the best way to check if it has been leaked.
2. Credential Theft
Since thejavasea.me leaks aio-tlp370 has appeared on the Internet, it is reasonable to discuss the possibility of user account compromise. In this context, it is important to note that such files often contain users’ usernames and passwords, allowing hackers to gain full access to their accounts.
I believe it is essential to advise readers to change their passwords, especially if they have reused the same credential on multiple accounts. Even if certain accounts were not hacked, attackers could use the information from thejavasea.me leaks aio-tlp370 to verify the passwords on other websites.
3. Privacy and Identity Concerns
The issue of identity theft is closely related to thejavasea.me leaks aio-tlp370. On the one hand, it is impossible to deny that such files can contain a lot of personal information that can be used by hackers. On the other hand, it would be a mistake to overestimate the threat posed by this particular leak.
I think it is essential to take a realistic look at the situation and remember that thejavasea.me leaks aio-tlp370 might not contain the information described in various articles. At the same time, it is necessary to protect oneself from potential threats posed by the file.
For example, users can delete unnecessary information from their accounts and ensure that the details of their accounts are not available to unauthorized people.
4. Legal and Ethical Risks
Thejavasea.me leaks aio-tlp370, like many other similar files, was created illegally. In this regard, it is reasonable to mention the legal and ethical risks associated with interacting with such files.
In particular, downloading and distributing thejavasea.me leaks aio-tlp370 can be illegal and violate personal privacy. Even though some people might argue that this file can be useful for research purposes, interacting with it can lead to serious consequences for one’s privacy.
As connected devices become more common, understanding the features of smart TVs, such as those covered in About ZO35-G25DA74 Model TV: Redefining Smart Viewing, is also important for evaluating their security and privacy.
How to Protect Yourself From Leak-Related Threats
The main rule in protecting oneself from threats related to thejavasea.me leaks aio-tlp370 is to avoid downloading the file. Users can also follow a few other tips that will allow them to keep their accounts secure.
Check Your Accounts Through Trustworthy Sources
If the user believes that their email address appears in thejavasea.me leaks aio-tlp370, then it is essential to check their accounts for unauthorized activity. I recommend visiting the website of the service used and changing the password.
At the same time, the user should be especially careful when interacting with websites offering to check their accounts against thejavasea.me leaks aio-tlp370 and other similar files. If a website asks the user to provide their passwords to scan their personal data, this is a malicious resource.
Change Reused Passwords
If the user has reason to believe that their data has been compromised, they should consider changing passwords. People can change the reused password to a more secure one or use a different password for each account.
In the latter case, it will be much easier to deal with the situation if one account is hacked because other accounts will have unique access details.
Enable Multifactor Authentication
I recommend that the user enable multifactor authentication to protect their accounts. Even if the attacker obtains the user’s password, multifactor authentication will prevent them from accessing the account.
Keep Devices Updated
The user should ensure that their devices are up to date to avoid potential security issues. This includes not only computers and smartphones but also other gadgets and programs. It is a good idea to enable the automatic update mode if there is no fear that it will interfere with work.
Be Careful With Phishing Attempts
People should be aware that phishing attacks can be used to obtain private information. Be especially careful when you receive an email requesting you to provide your information to access confidential data about your account or other personal matters.
What Businesses Can Learn From the AIO-TLP370 Discussion
Though thejavasea.me leaks aio-tlp370 have not been verified, this situation brings up several cybersecurity issues companies should think about. Firstly, I want to mention how important it is to keep track of confidential data and make sure it is not available to unauthorized users.
Companies must have incident response plans that will help reduce adverse outcomes if the data leak still happens. Secondly, it might also be helpful to devise a cybersecurity strategy aimed at detecting possible problems in the early stages. I believe it is also a good idea to reinforce the infrastructure and be careful when working with third-party solutions.
In conclusion, I believe that companies should be especially careful when using software programs since they are the most vulnerable points in the cybersecurity system.
How to Evaluate Claims About thejavasea.me Leaks AIO-TLP370
When researching thejavasea.me leaks aio-tlp370 , I noticed that many sites publish similar information on this topic. At the same time, only a few of them provide credible data that allows the user to draw reliable conclusions.
Therefore, in my opinion, it is essential to understand what to do when encountering such information.
First, it is a good idea to separate unsubstantiated claims from verified facts.
Second, it is helpful to look for additional data supporting the claims. For example, if a site states that thejavasea.me leaks aio-tlp370 has a large amount of information, then it must be possible to provide statistics or specific data.
Finally, the site should show the difference between facts and opinions and avoid publishing misleading information.
Cybersecurity risks can also affect supply chains, making it essential to understand how ProcurementNation .com Shipping: Your Guide to Efficient Logistics addresses logistics and operational efficiency.
Final Thoughts
The debate on thejavasea.me leaks aio-tlp370, which occurred on thejavasea.me forum, proves that it is vital to take a calm and unbiased view on the matter. Accordingly, the major lesson is to be safe about one’s own accounts and data.
For the common users, it means no opening of suspicious files and links, applying reliable and unique passwords, checking the activity of their accounts regularly, and being cautious about others’ contacts. Meanwhile, companies must focus on keeping users’ data safe and having a strategy to react in case of an incident.